Guides
How to Verify a Firewall Change After the Change Window
You verify a firewall change by comparing what the firewall now contains with what the ticket asked for, and then proving with traffic that the change works and nothing else moved. Four checks do that once the engineer has finished: a configuration diff against the state before the window, a placement check, tests of the allowed flow and of flows that must stay blocked, and a log review a day later. Each result goes on the ticket.
Verification is not the application team saying it works. That proves one flow. It says nothing about a second rule the engineer touched in the same session. "No more, no less" is two questions: is everything the ticket asked for present, and is anything present that it did not ask for? The diff answers both. The traffic tests show whether the result behaves.
This post covers the step after the window closes. Checking a change before it is made is in firewall rule impact analysis, and who may sign it off is in approval chains and separation of duties. The whole process is in the firewall change management guide.
Why is "it works" not proof that the change was correct?
A change can pass its own test and still be wrong in three ways. It can contain more than the ticket asked for, such as a widened object or a second rule. It can sit in the wrong place in the rule order. Or the test can look at the wrong surface. In the carrier outage described in our post on firewall change records as court evidence, initial testing reportedly showed normal calls connecting while the emergency calling path was down. The test checked what was meant to work and missed what could break.
NIST SP 800-53 asks for verification after a change, not only testing before it. Enhancement CM-4(2) says: "After system changes, verify that the impacted controls are implemented correctly, operating as intended, and producing the desired outcome with regard to meeting the security and privacy requirements for the system." Enhancement CM-3(2) asks organizations to "Test, validate, and document changes to the system before finalizing the implementation of the changes." Both texts cover systems in general. In our reading, for a firewall the "impacted controls" are the rule you changed and every rule that shares its objects or sits next to it.
What do you write down before the change window?
Write the expected result before the engineer starts: the exact rules, objects and positions the change should create, alter or remove, plus a list of what must stay untouched. Then export the running configuration as the before-snapshot. Without both, nobody can show "no more, no less" later, because the reference point for "more" exists only in someone's memory.
The expected diff is short. For an added rule it is one row: name, source, destination, service, action, logging, position. For a removal it is the rule and the objects that go with it. Have the approver read it during approval, so that the ticket and the expected diff say the same thing. Take the snapshot immediately before the first command, not the night before, or another engineer's change in between will show up as yours. Where the platform keeps per-rule hit counters, export them with the snapshot. You need them for the day-after check.
How do you prove the change did exactly what the ticket asked?
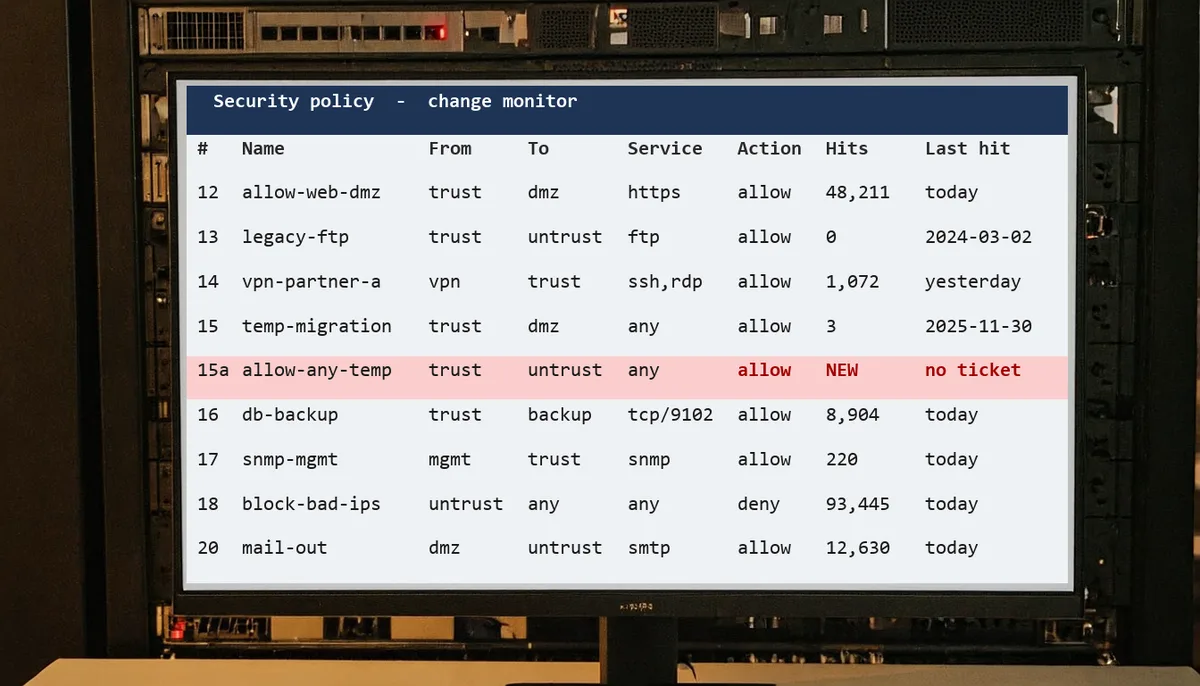
Export the running configuration after the change, compare it with the before-snapshot, and sort every difference into one of three buckets: on the ticket and present, on the ticket and missing, present but not on the ticket. Only the first bucket passes. A missing item means the change is incomplete. An extra item is a change nobody approved, even when the engineer meant well.
Compare rules, not raw text. A text diff of a firewall export fills up with timestamps, reordered objects and generated IDs, and a reviewer who sees hundreds of changed lines stops reading. Normalise the export first, or diff the policy model instead. Also confirm that you pulled the active configuration. On platforms with a separate commit or save step, the pending and the running configuration can differ, and the diff is only as good as the file behind it.
The most common miss is the shared object. If the engineer edits an address group to make the new rule fit, no rule line changes, yet every other rule that uses the group now matches different traffic. List every rule that references an edited object and treat each one as part of the change. The table shows what to look for by change type.
| Ticket asked for | The diff must show | Typical "more" to look for |
|---|---|---|
| Add a rule | One new rule with the ticket's source, destination, service, action and logging setting | A new or widened object created to make it fit; a second rule "for the return path"; a catch-all left behind |
| Modify a rule | Old and new values for exactly the fields the ticket names | Other fields changed in the same edit, such as the logging profile or an any that stayed |
| Remove a rule | The named rule gone, its neighbours unchanged | The wrong one of two similar rules removed; objects deleted that other rules still use |
| Move a rule | A position change and nothing else | Rules between the old and the new position that now match different traffic |
| Edit an object | The one object, plus the list of rules that reference it | Every referencing rule now behaves differently |
For a modification, record the old and new value of each named field. If three fields changed and the ticket named one, the other two are findings.
Is the rule in the right place?
Check the position of every added or moved rule. Firewalls evaluate rules in order and, on most platforms, the first match decides. A new allow rule below an older deny that matches the same flow never fires, and a new rule above other rules can take over traffic they used to handle. Confirm that no earlier rule matches the flow with a different action, and that the new rule does not shadow anything below it.
The analysis you ran before the change can run again on the after-state, which is cheap and catches slips in the implementation. The question changes from "what would this do?" to "is this what it does?" The method is in firewall rule impact analysis.
Which traffic tests prove the result?
Test the allowed flow, then test what must still be blocked. One positive test shows the new access works. Negative tests show the rule is not wider than the ticket: the same source to a different port, a host just outside the named source, and one unrelated critical service. Run them from the real source segment and keep the firewall's own log line that shows which rule matched. A screenshot of a working application is not evidence about the rule.
| Test | Example | Passes when | Keep as evidence |
|---|---|---|---|
| Positive | The ticket's source to destination and port | The connection succeeds | Session or log entry naming the new rule |
| Port neighbour | Same source and destination, another port | Blocked, or matched by the rule that should match | Log entry with the matching rule |
| Source neighbour | A host just outside the named source | Blocked, or matched by the intended older rule | Log entry with the matching rule |
| Critical service | The service most likely to share objects or path, such as DNS or authentication | Behaves as before the change | Test result with time |
NIST SP 800-41 Rev. 1 describes the aim for a new firewall: traffic the policy allows is permitted and all other traffic is blocked, and "Verification of the ruleset should include both reviewing it manually and testing whether the rules work as expected." The same document calls it an important task to "perform periodic testing to verify that firewall rules are functioning as expected." Reading the rules and testing them check each other, which is the same pairing as the diff and the traffic tests above.
One caution from the carrier case: make sure a failure would show up where you look. If the deny log for the tested flow is switched off, a clean log proves nothing.
What should you check the day after?
Check the rule's hit counters and the neighbouring deny logs 24 hours after the change. The new rule should show hits from the expected sources and no others, and the deny counts on the rules around it should not have jumped. This catches what a test in the same hour cannot, such as a batch job that runs at night.
After a removal, wait for a full business cycle before you call it clean. A rule can sit idle for weeks and still carry the monthly job, which is why a clean first week proves little; see firewall rule decommissioning. Then compare the next scheduled configuration export with your after-snapshot. A difference nobody ticketed is a different problem, covered in drift detection for unauthorized firewall changes.
What do you record for the auditor?
Record the expected diff, the before and after snapshots, the classified diff, every test with its log evidence, who verified and when, and the day-after result, all attached to the ticket. An auditor should be able to retrace the change without asking anyone. The standards ask for the record, not for this exact layout.
NIST SP 800-41 says that "a log should be kept of all policy decisions and ruleset changes". The German BSI module NET.3.2 Firewall requires, in requirement A14, that all configuration changes are documented, in particular changes to the firewall's rule set (our translation). In requirement A2 it adds: "Es MÜSSEN Zuständige benannt werden, die Filterregeln entwerfen, umsetzen und testen" (our translation: responsible persons must be named who design, implement and test filter rules). NIST CM-3 requires organizations to retain records of configuration-controlled changes for an organization-defined period.
| Field | What it proves | Basis |
|---|---|---|
| Ticket ID and approved revision | What was asked for and approved | Our recommendation; see approval trail |
| Expected diff, written before the window | What "no more, no less" meant for this change | Our recommendation |
| Before and after snapshots with time | The two reference points | Our recommendation; related: NIST SP 800-41 (log of ruleset changes), BSI NET.3.2.A14 |
| Classified diff | Every difference sorted as expected, missing or extra | Our recommendation |
| Tests: source, destination, port, expected, actual, matching log line | Behaviour is as intended | NIST CM-4(2); NIST SP 800-41 |
| Verifier and time | A named person checked it, ideally not the implementer | Our recommendation |
| Result: pass, fail, or pass with a named exception | The decision | NIST CM-3 (document change decisions) |
| Day-after check | No late side effects | Our recommendation |
| Retention period | The record is still there when the audit comes | NIST CM-3 |
What if the verification fails?
Decide inside the window whether to fix forward or roll back, and record both the failure and the fix on the same ticket. Never close the ticket and repair quietly. A failed first check that is documented and corrected shows a control that works. The same fault corrected without a record looks like an unauthorised change in the next audit.
If the diff shows something extra, treat it as an unapproved change: remove it, or approve it afterwards through your emergency path with a named second approver. Rollback mechanics are in the emergency change that never gets rolled back.
Checklist: after-window verification
- The expected diff exists in writing before the window and matches the ticket.
- A before-snapshot was taken immediately before the first command.
- The after-snapshot comes from the active configuration, not a pending one.
- Every difference is sorted as expected, missing or extra; extras are resolved.
- Edited shared objects are listed with every rule that references them.
- Rule position is checked against earlier and later rules.
- One positive and at least three negative tests ran from the real source segment.
- Each test has the firewall's own log line as evidence.
- Someone other than the implementer reviewed the result, where staffing allows.
- Hit counters and neighbouring deny logs were checked after 24 hours.
- The record sits on the ticket and is kept for the period your regulator or policy sets.
How we checked this
On 22 November 2026 we read NIST SP 800-53 Rev. 5 controls CM-3 and CM-4 as reproduced on csf.tools, NIST SP 800-41 Rev. 1 (September 2009) and the BSI IT-Grundschutz module NET.3.2 Firewall (Edition 2023). We did not quote PCI DSS here. The four checks, the three buckets, the test set and the 24-hour check are our own recommendation.
Today FwChange's automated after-change check covers rule removals; for added and modified rules the steps above stay manual. FwChange reads the firewall with read-only accounts and records what it finds. Your engineers make the change. Book a demo.